
For SMBs and large enterprises alike, in every sector
Less risk.Fewer surprises.Fewer tools to pay for.
FortaRisks shows executives where their company is exposed, in its systems, its plants and at its suppliers, then what to fix first. You get the proof that risk is going down, for your board, your customers and your insurer.
Your domain name is enough. Report within 48 hours, explained by an expert.
See the product tour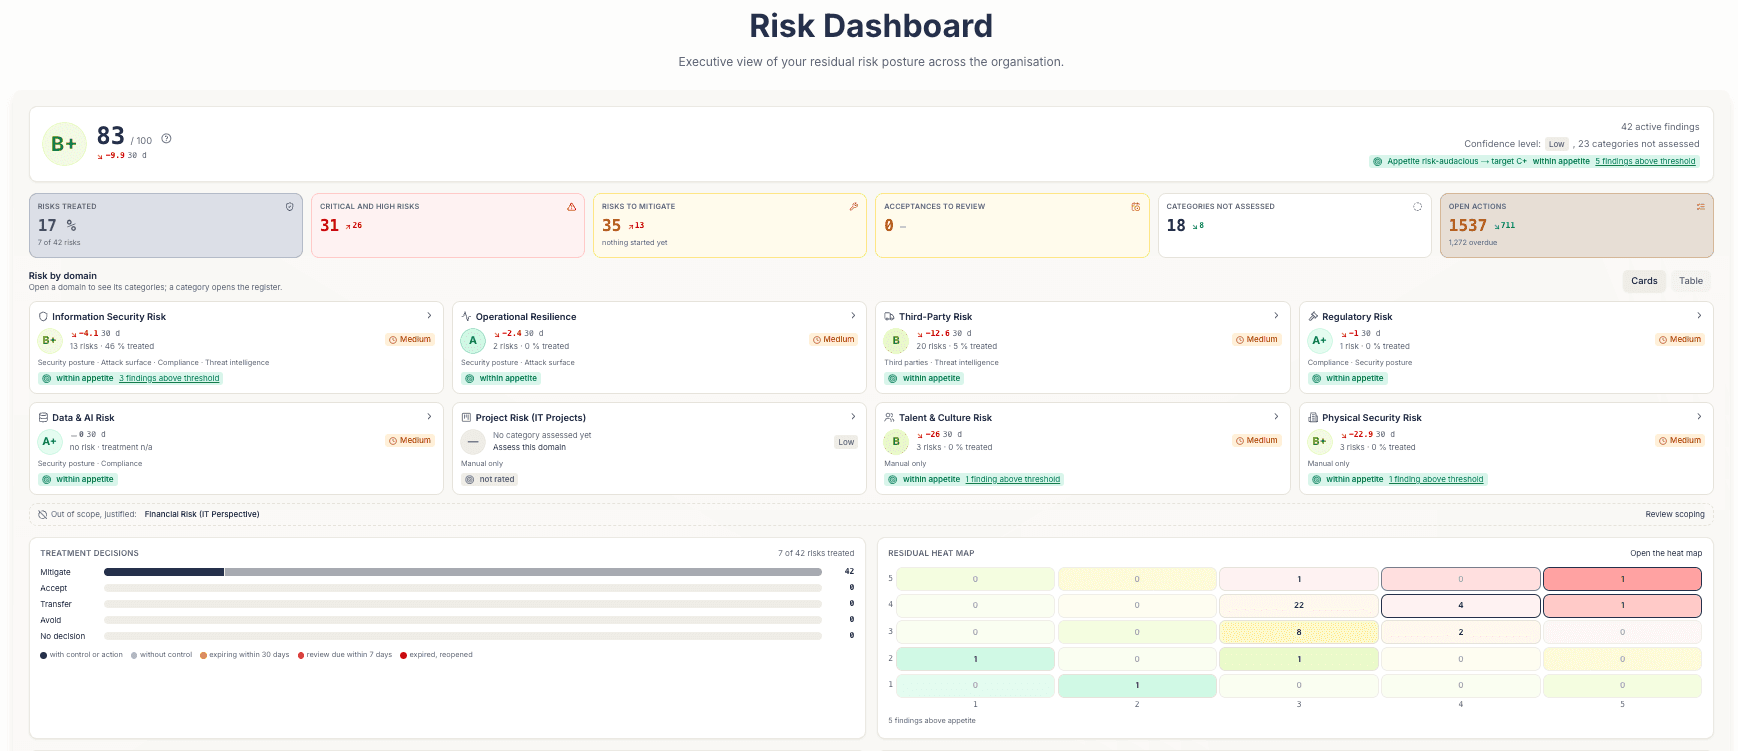
- The overall risk score and its trend
- Risk by domain
- The residual risk heat map
Forta Cockpit, the risk dashboard. Screenshot of the platform.
From threats to proof
Each module feeds the next one. That link is what replaces three software tools and a spreadsheet.
- 1. Threats
Forta Radar
The threats that target your sector and your technologies.
- 2. Exposure
Forta Exposure and Forta Suppliers
Where they can get in, at your company and at your suppliers.
- 3. Register
Forta Cockpit
Every finding becomes a ranked risk, before and after your controls.
- 4. Actions
Forta Actions
Every risk becomes an action, with an owner and a due date.
- 5. Proof
Forta Compliance
The proof that risk is going down, for the board, your customers, your insurer and the auditor.
Cybersecurity has become a condition for doing business.
It is no longer just the IT department's concern. Your customers, your insurer and the law ask for proof, and your plants are now connected to the Internet.
A customer requires it
A security questionnaire to fill in, a clause added to the contract. With no evidence, the contract waits.
See howYour insurer asks for it
Insurers price on what you can demonstrate, no longer on a declaration.
See howQuebec Law 25 names you
By default, Law 25 makes the most senior executive the person responsible for protecting personal information.
See howYour plants are connected
One maintenance access left open is enough. Industrial equipment reachable from the Internet can be spotted from the outside, by you or by an attacker.
See how
Data in five tools, the full picture nowhere
An industrial group tracks its risk, its compliance gaps and its suppliers in separate tools, and its team spends weeks stitching spreadsheets together. Once brought together, the risk, the gaps and what is moving at suppliers can be read in one place.
Exposures found once a year
A distributor only found its exposures at the annual penetration test. With continuous monitoring, it sees its attack surface the way an attacker does, keeps only the threats that target it and works a short list rather than a queue of alerts.
For SMBs and large enterprises alike, in every sector.
Whether you manufacture, distribute, build or provide services, the need is the same: see where you are exposed, know what to fix first, and be able to prove it. Three situations we often see:
Manufacturers
Your plants are connected and your customers ask for proof. You see what is exposed, industrial equipment included.
Multi-site companies
Several sites, several teams, sometimes acquisitions. One view of exposure and gaps, by entity or by asset group.
Prime contractors
Your suppliers are part of your risk. You monitor them continuously, beyond their answers to a questionnaire.
Six modules, one platform.
Threats, exposure, suppliers, compliance, risks, actions: six modules connected to each other. What one module detects feeds the others, all the way to the proof that risk is going down.
Forta Radar
Threat intelligence (CTI)
Know which threats target your sector before they strike.
Explore moduleForta Exposure
External attack surface (EASM), plants included
See your company the way an attacker sees it.
Explore moduleForta Suppliers
Third-party risk (TPRM)
Spot the suppliers that expose you, and answer your customers only once.
Explore moduleForta Compliance
Frameworks and requirements (GRC)
Measure once, prove it to everyone who asks.
Explore moduleForta Cockpit
Risk register, for decision-makers
Your risks ranked, and the proof that risk is going down.
Explore moduleForta Actions
Action Center, for operational teams
Every morning, the short list of what to fix, prioritized and with due dates.
Explore module
Plus everything that connects them.
Give your team their time back.
FortaRisks replaces a stack of overlapping tools and turns scattered signals and manual compliance work into one short, ranked list of actions. Fewer licences, less noise, fewer manual hours, defensible decisions.
$100K+
Of cyber tooling saved every year
5 to 10
Actions a day, instead of 2,000 alerts
60%
Less GRC effort
Weeks
To prepare your SOC 2 Type II
Orders of magnitude estimated by FortaRisks; your results depend on your scope.
We correlate your posture with threats, exposure and third-party risk.
Most tools show you threats or your posture, never the link. FortaRisks connects them all, so 2,000 raw alerts a day become 5 to 10 prioritized actions.
Live threat intelligence
100+ sources aggregated continuously, including MITRE ATT&CK, CISA KEV and EPSS.
Continuous correlation
Active campaigns and exploited CVEs mapped to your real exposure and controls.
Prioritized action
A short, ranked list of what to remediate, with the business context behind it.
50M+
Signals analyzed every day
100+
Threat intelligence sources
2,000+
Threat actors tracked
40+
Compliance frameworks
Aligned with the frameworks your teams already use
- Quebec Law 25
- CPCSC
- IEC 62443
- NIST CSF 2.0
- ISO 27001
- SOC 2
Stop guessing where your risk is.
In a 30-minute demo, see what would actually bring your risk down, or take the self-guided product tour first.
A platform, with a team behind it.
FortaRisks does not ship with a link to the documentation. Your assessments, your roadmap and your priorities are built with cyber risk practitioners who know your account, your sector and what you have already fixed.
One person, not a ticket number
The same team follows you over time. You never have to explain your environment again from scratch.
A critical exposure never stays a finding
When a critical exposure shows up on your attack surface, or your risk drifts seriously, we reach out and help you deal with it.
Getting started happens with you
Guided onboarding, scaled to your plan: scope, frameworks, first assessments. You never start from a blank page.
Workshops with our experts
Posture review, audit preparation, roadmap trade-offs: up to five workshops a year, run by practitioners.
And when you write to us, a human answers, on every channel.
Works with the tools you already use.
- Signed webhooks
- Slack
- Microsoft Teams
- STIX 2.1 export
- Email digests
- XLSX and PDF exports
- Microsoft 365
- Microsoft Entra ID
- Microsoft Defender
Platform data stays in Canada.
The question is not only where your data is stored, but who can be compelled to hand it over. A vendor subject to US law can be, wherever it hosts. FortaRisks is a Canadian company, and the data you entrust to the platform is hosted in Canada. US or EU hosting is possible from onboarding, if your organization requires it.
The CLOUD Act follows the provider, not the server
A US vendor stays subject to the CLOUD Act wherever it hosts. FortaRisks platform data is hosted in Canada, by a Canadian company.
30 minutes to know what to fix first.
A member of our team walks you through FortaRisks on threats relevant to your sector, and you leave with your priorities.
Frequently asked questions
Is FortaRisks one platform or several tools?
One platform. Six connected modules: Forta Radar, Forta Exposure, Forta Suppliers, Forta Compliance, Forta Cockpit, the risk register for executives, and Forta Actions, the Action Center for the teams. One console, instead of stitching dashboards together.
Which frameworks do you support?
40+, including NIST CSF 2.0, ISO 27001, SOC 2, NIS2, DORA and Quebec Law 25, mapped through 1,534+ SCF controls. The full list is on the Frameworks page.
Do I need to buy extra threat feeds?
No. 100+ intelligence sources are included in your plan, aggregated and deduplicated.
Do you see exposed industrial equipment?
Yes. Industrial equipment reachable from the Internet is identified read-only, on 15+ ports, without touching production.
Where is my data hosted?
In Canada by default. FortaRisks is a Canadian company, and the data you entrust to the platform is hosted there. The US CLOUD Act, for its part, binds vendors subject to US law wherever they host. US or EU hosting remains available at onboarding if you need it.
Are we on our own with the platform?
No. Getting started happens with you, guided according to your plan. After that you keep the same point of contact, expert workshops through the year, and a direct line when a critical exposure appears. Advanced and Enterprise add priority support, and Enterprise a dedicated CSM.